[ccpw id="39382"]

Rapid7 Uncovers Fraud Campaign Using Roughly 885,000 Phone Numbers to Identify Crypto Users
A large-scale cryptocurrency fraud operation used hundreds of thousands of phone numbers to identify crypto account holders before targeting them with fake support interactions and counterfeit wallet software designed to obtain recovery phrases, cybersecurity firm Rapid7 said.
Dubbed Operation ASTERIX, the campaign combined account-validation tools with phishing emails and vishing calls. Rapid7 said the operators also deployed fraudulent versions of Trezor, Ledger and Exodus wallet applications as part of the scheme.
The scale of the targeting was visible in data examined by the cybersecurity firm. The operation handled about 885,000 phone numbers overall. In a German dataset containing 316,002 numbers, the operators confirmed 43,066 as linked to Crypto.com accounts.
Once accounts were identified, the operators added personal information to their target records, allowing them to pose more convincingly as customer-support representatives.
Rapid7’s investigation also found the operators incorporating AI coding tools into their workflow. GitHub Copilot and Claude Code were used for tasks including handling target data, creating and troubleshooting malicious software, and setting up phishing infrastructure.
When Claude rejected requests involving code obfuscation, an operator turned to Kimi and tried to circumvent its safeguards using a custom jailbreak prompt. Rapid7 was unable to establish whether the bypass attempt worked.
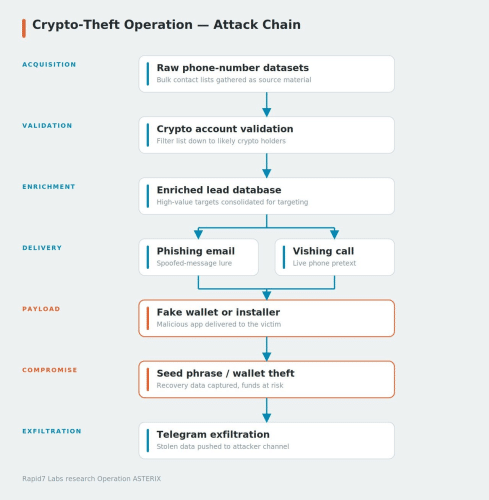
Source: Rapid7 Labs Research